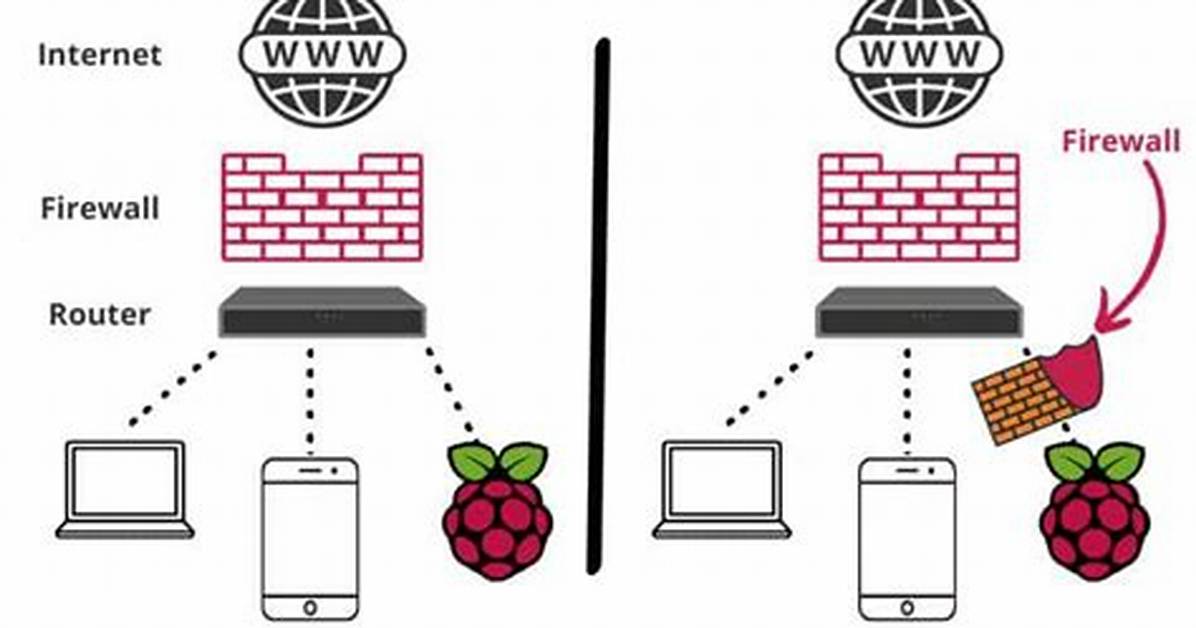
Setting up a Raspberry Pi firewall is essential to ensure your device remains secure while allowing necessary traffic through specific ports. Whether you're managing a home network or running a server, understanding how to configure your Raspberry Pi firewall properly can prevent unauthorized access and protect your data. This guide will walk you through everything you need to know about Raspberry Pi firewall configuration and how to allow specific ports.
In today's interconnected world, securing your devices is more important than ever. A Raspberry Pi can be used for various purposes, from acting as a home media server to running complex applications. However, without proper security measures, your Raspberry Pi could become vulnerable to attacks. Configuring a firewall is one of the most effective ways to safeguard your device.
This article will provide a comprehensive overview of Raspberry Pi firewalls, focusing on allowing specific ports to ensure smooth communication while maintaining security. We'll cover everything from basic configurations to advanced settings, ensuring you have the knowledge to protect your Raspberry Pi effectively.
Introduction to Raspberry Pi Firewall
A Raspberry Pi firewall is a critical component for securing your device. It acts as a barrier between your Raspberry Pi and the outside world, controlling incoming and outgoing traffic based on predefined rules. By configuring a Raspberry Pi firewall, you can specify which ports are open and which are closed, ensuring only authorized traffic is allowed.
Firewalls are essential for any network-connected device, but they are especially important for Raspberry Pi, which is often used for sensitive applications. Whether you're running a web server, SSH service, or media server, understanding how to configure your Raspberry Pi firewall can prevent unauthorized access and protect your data.
One of the most common tasks when setting up a Raspberry Pi firewall is allowing specific ports. For example, if you're running a web server, you'll need to allow traffic on port 80 (HTTP) and port 443 (HTTPS). Similarly, if you're using SSH for remote access, you'll need to allow traffic on port 22. This article will provide step-by-step instructions for configuring your Raspberry Pi firewall and allowing specific ports.
Why Use a Firewall on Raspberry Pi?
Using a firewall on your Raspberry Pi is crucial for several reasons. First and foremost, it enhances security by blocking unauthorized access to your device. Without a firewall, your Raspberry Pi could be vulnerable to attacks from malicious actors who may attempt to exploit open ports or vulnerabilities in your software.
In addition to security, a firewall can also improve performance by filtering out unnecessary traffic. By allowing only the necessary ports and blocking everything else, you can reduce the load on your Raspberry Pi and ensure it runs smoothly.
Lastly, a firewall provides peace of mind. Knowing that your Raspberry Pi is protected from potential threats can give you confidence in using it for various applications, whether it's a home automation system, a media server, or a development platform.

